The challenge
Compliance requires complete, protected logs at scale
NIS2, DORA, ISO 27001, SOC 2 and PCI DSS expect organizations to collect the right logs, protect them from tampering, retain them, and produce them on request. Keeping everything in a SIEM is expensive. Many organizations also cannot let data leave their country or region. And when a log source silently stops sending, nobody notices until the auditor asks.
The solution
DataStream as the compliance layer for security logs
Collect from 300+ sources
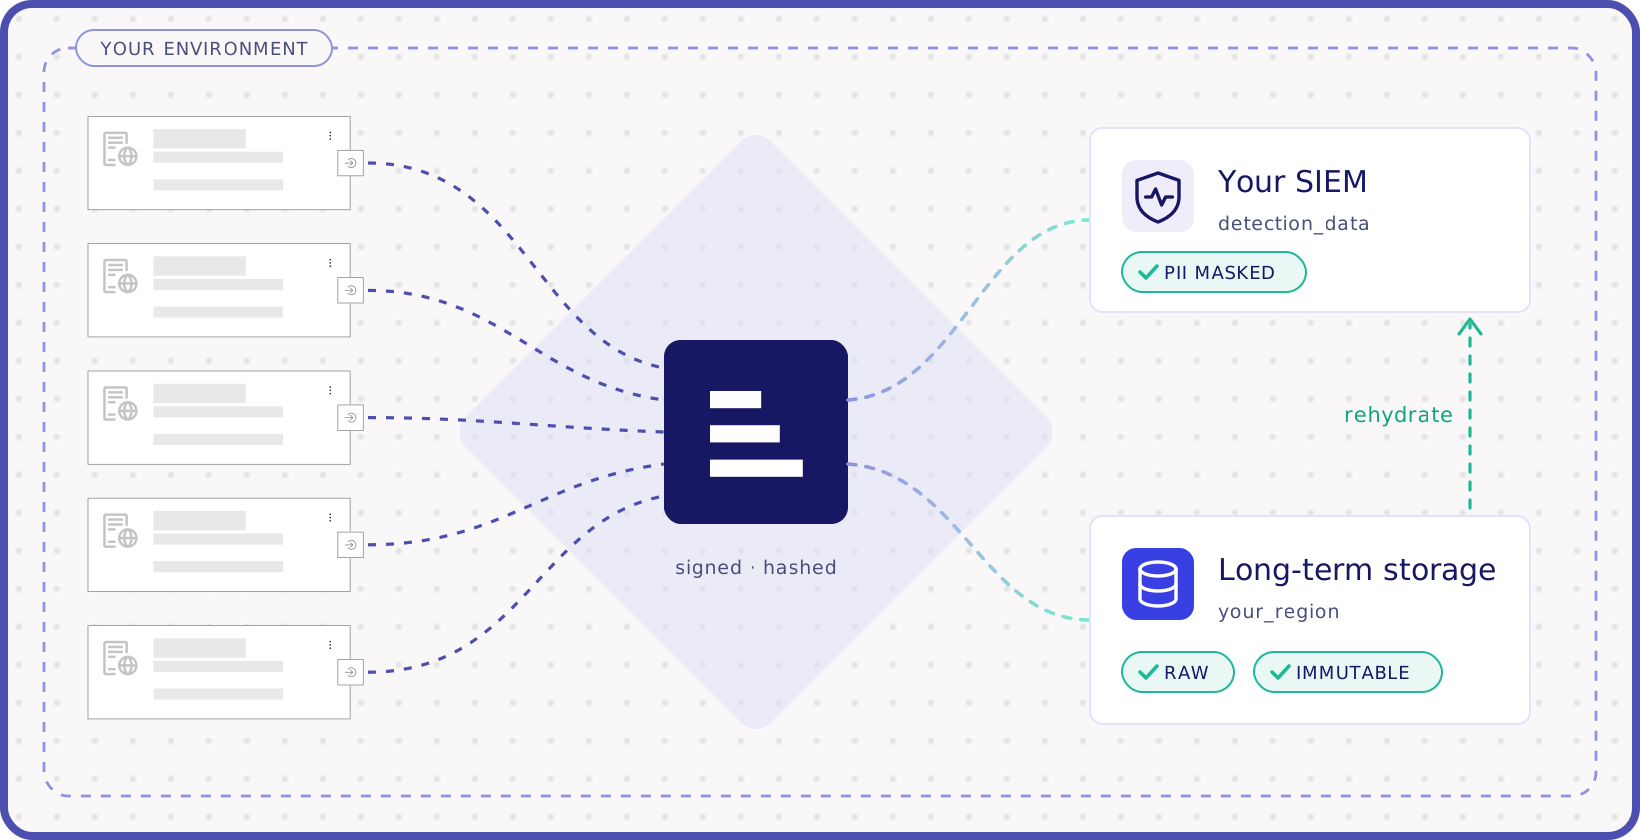
DataStream collects from 300+ sources, agentless or agent-based. Its write-ahead log architecture prevents data loss, even when a destination is temporarily unavailable.
Know immediately when logging fails
DataStream monitors every source, every deployment and every destination, with health views for throughput, queues and delivery. If a device stops sending or a destination stops receiving, you get an alert. You can show auditors that every source is reporting.
Store raw logs in your own storage
Audit retention does not require normalization. DataStream can keep the original raw message as compressed Parquet, typically 80 to 90% smaller, in the storage and region you choose, encrypted in transit and at rest.
Protect logs from tampering
Data collected by agents is signed and checked on arrival, and records can be hashed before storage. Immutable storage keeps archived logs from being changed or deleted before their retention period ends.
Mask personal data per destination
Mask PII fields for each destination that needs it. You keep the security value of your logs, and each destination stores only the personal data it needs, as GDPR’s data minimization principle requires.
Rehydrate fast when it matters
When an auditor asks for evidence or an incident requires history, DataStream rehydrates the data you need into your SIEM or analytics tool. You pay SIEM ingestion only when you use the data.
What regulators expect
What NIS2 expects you to log
The NIS2 implementing regulation (EU) 2024/2690 sets logging requirements for cloud, data centre and DNS providers, managed service providers, MSSPs and other digital providers it lists. Logs must be backed up, kept for a predefined period and protected against unauthorized access or changes. Where appropriate, they must include the 12 types below, and DataStream can collect them from the systems that produce them.
Identity and access
- Creation, modification or deletion of users, and extension of permissions
- Access to systems and applications
- Authentication events
- All privileged access, and activity of administrative accounts
Network and security tools
- Inbound and outbound network traffic
- Event logs and logs from security tools such as firewalls, IDS and antivirus
- Access to and use of network equipment
Systems and logging
- Access to or changes in critical configuration and backup files
- Use of system resources and their performance
- Activation, stopping and pausing of logs
Facilities
- Physical access to facilities
- Environmental events
Key benefits
Why this approach works

Who it’s for
Built for regulated organizations
Many regulated organizations answer to several frameworks at once, and their logging requirements overlap. DataStream supports the logging requirements in NIS2, DORA, PCI DSS and HIPAA, and the ISO/IEC 27001 logging controls that BIO2 and BSI IT-Grundschutz align with. Masking personal data per destination supports GDPR data minimization.
Frequently asked questions
Do we need to normalize logs for audit retention?
No. For audit purposes DataStream can keep the original raw message. Normalize only the data you send to your SIEM for detection.
How do we prove logs were not altered?
With LogChain, agents sign the data they collect, and DataStream checks every upload before it accepts it. This proves nothing changed between the agent and the pipeline. Before storage, a SHA-512 hash of the fields you choose can be added to each record, which helps you detect later changes. With immutable storage, archived logs can’t be modified or deleted before the retention period you set.
How do we know no logs are missing?
DataStream alerts on individual devices, deployments and destinations. If a source stops sending or a destination stops receiving, your team is notified right away.
Does storing raw logs conflict with GDPR?
Not when personal data is handled correctly. DataStream masks PII fields for each destination that needs it, so you retain security value without keeping more personal data than needed.
Where is the data stored, and does anything leave our environment?
Data is stored in the storage you choose, in your own environment: Amazon S3, Azure Blob Storage, Google Cloud Storage or on-premises object storage. Your data never leaves your environment.
Who can access the logs and the pipeline?
DataStream has role-based access control and keeps audit logs of all configuration changes, so you can show auditors who changed what and when.
Does DataStream make us NIS2 compliant?
No tool does that on its own. NIS2 covers governance, processes and people. DataStream covers the logging, protection and evidence requirements, and sends logs to the storage where you set retention.
What happens if a destination is unavailable?
DataStream buffers data with its write-ahead log architecture and delivers it once the destination is back.
Talk to our experts
Schedule a technical session with our engineering team to review your logging, retention and sovereignty requirements and see how DataStream meets them.
Try DataStream
Try DataStream in your environment and see how it simplifies compliant log retention in weeks.
Start now